Organisations our team has delivered for
End-to-end cyber security and GRC services
One partner from first risk assessment to automated, audit-ready compliance.
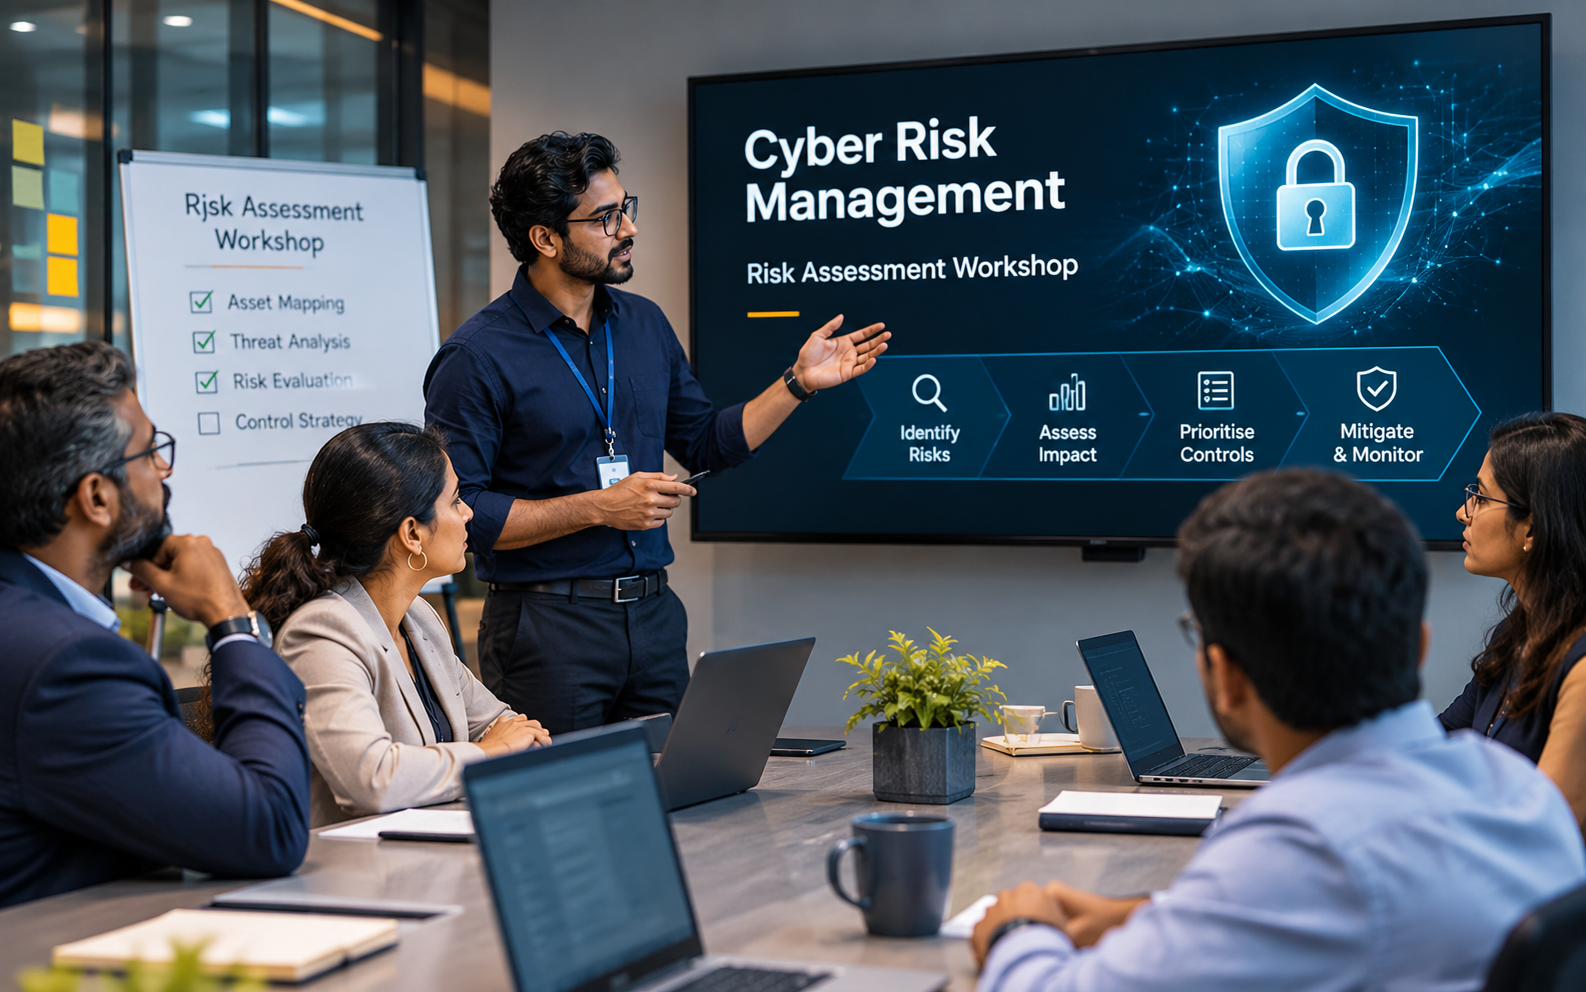
Cyber Risk Management
Identify, measure and prioritise the risks that matter, across your systems, data and vendors.
Discuss a risk assessment- Privacy Risk Assessment
- Data Privacy Risk Assessment
- Cyber Security Risk Assessment
- Policies & Standards Development
- Gap Assessment & Control Mapping
- Third-Party Risk Management
Technology Transformation
Move GRC off spreadsheets. We implement, integrate and migrate the platforms that automate risk and compliance.
Discuss GRC automation- GRC AutomationArcher IRM, ServiceNow, OneTrust, ZenGRC
- IntegrationJira, PeopleSoft
- Cloud TransformationAWS, Azure
- Platform ImplementationDesign, build, deploy, support
Technology Audit
Independent audits and readiness reviews against the frameworks your regulators and customers ask for.
Discuss an audit- ISO
- NIST
- PCI
- COBIT
- FedRAMP
- IRAP
- GDPR
- NYDFS
- Internal Audits
Cyber Security Consulting
Strategic security leadership and roadmaps, on demand, without the full-time CISO cost.
Discuss vCISO support- GRC Roadmap
- Privacy
- Control & GRC Framework Development
- Gap Remediation
- vCISO (Virtual CISO)
Training
Upskill your team on GRC platforms and globally recognised security certifications.
Enquire about training- Archer GRC
- ServiceNow
- CISA
- CISSP
- CISM
- CIPP
- Security+
- AWS Solution Architect
- Azure Solution Architect
Big 4 depth. Boutique attention. Offshore economics.
Former Big 4 professionals
Consultants who have led GRC programmes for banks, insurers and multinationals.
Cost-effective offshore model
Onshore oversight with offshore delivery maximises value without compromising quality.
Standardised, flexible delivery
A repeatable framework adapted to your industry and evolving regulatory demands.
Regional presence
Headquartered in Singapore, with teams in India and Dubai close to your business.
The GRC specialists behind your programme
Lead architects and implementers who have delivered GRC projects for national and multinational clients across the globe.
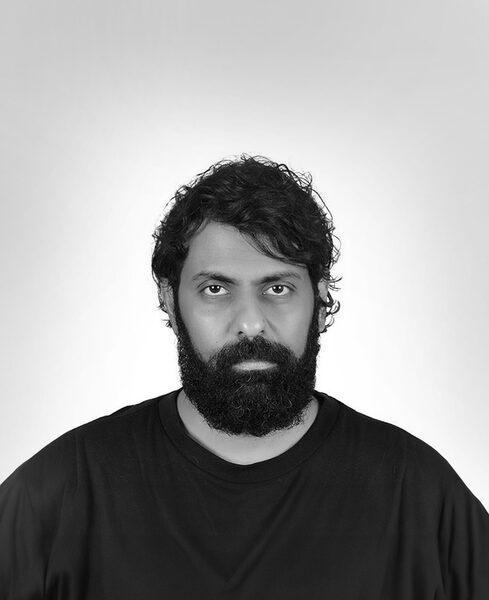
Manu Shrivastava
- Archer IRM, OneTrust, BWise
- Led teams of 80+ resources
- ISO, SOX, HIPAA, NIST CSF, PCI DSS
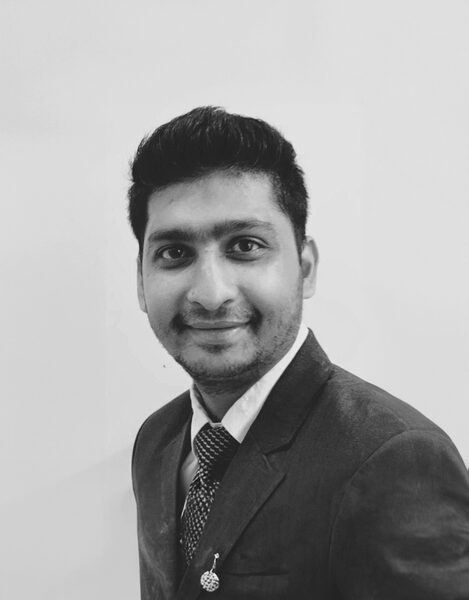
Madhup Agarwal
- Lead architect and implementer, Archer IRM
- End-to-end GRC deployment
- ISO 27001, HIPAA, FFIEC, NIST mapping
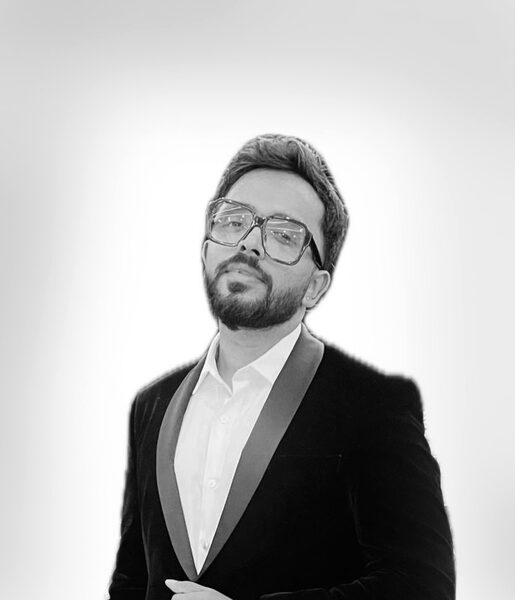
Vishnu Kumar
- Archer IRM and OneTrust implementation
- Onshore and offshore deployments
- Global GRC project delivery
Leadership & Client Partners
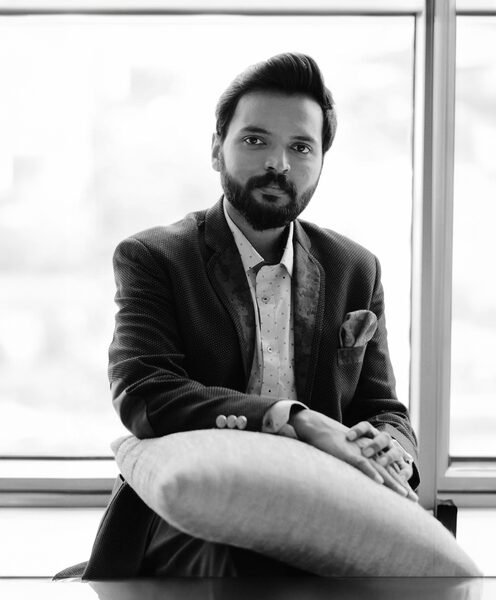
Vinay Bharadwaj
- 19+ years across banking and consulting
- 9 years in investment banking, strategy & digital for Singapore and global markets
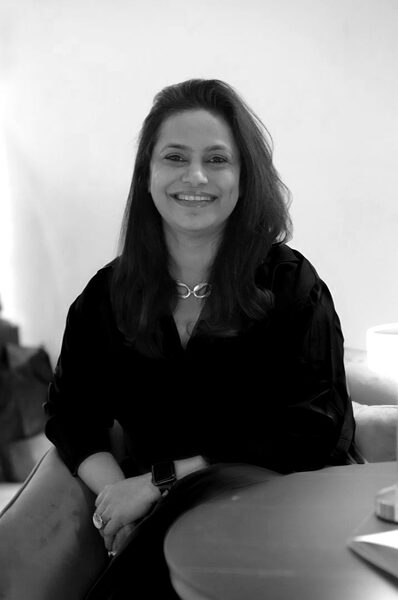
Smita Uchil
- Co-founder, Pinnacle online ticketing platform
- 12+ years in business and event management
Trusted by partners and industry leaders
Since our partnership with Archer Advisory began in April 2022, we've successfully executed around twelve projects in India. Archer Advisory has played a pivotal role in showcasing the capabilities of Archer to our shared customers.
I have known Manu since 2008 and Madhup soon after. If they were part of the project team, I wouldn't have to worry about anything. It would be good quality work and on time. If I needed external help, I would blindly go to them.
See our full capability deck
Browse the slides below. Share your details to download the PDF for your team.